Pre-Launch Assurance
Before launching a new product, customer portal, or major feature release. Identifies vulnerabilities while remediation is cheapest - pre-production.
Assess AWS, Azure and Google Cloud permissions, exposed resources and configuration. Get practical remediation advice.
 Secured 100+ organisations
 4.9
 Clutch
single environment
Definition
See how cloud penetration testing assesses identity permissions, exposed services and risks across connected cloud resources.
Cloud penetration testing is a controlled, manual security assessment where CREST-certified ethical hackers simulate real-world attacks against your AWS, Azure, Google Cloud, Entra ID, cloud networks, IAM, storage, Kubernetes and serverless environments. The goal is to identify exploitable cloud weaknesses such as excessive permissions, exposed storage, public services, weak identity controls, insecure secrets and privilege escalation paths before attackers find them.
Unlike automated cloud posture scanning, a true cloud penetration test validates whether misconfigurations can be exploited, chained and used to access sensitive data or escalate privileges. A skilled tester turns identity, network, storage and workload weaknesses into a short, prioritised list of confirmed, exploitable findings with proof-of-concept evidence, business impact and remediation guidance.
For Australian businesses, cloud penetration testing is strong evidence for ISO/IEC 27001:2022 controls A.8.8 and A.8.29, SOC 2 Trust Services Criterion CC7.1, PCI DSS Requirement 11.4, APRA CPS 234, and customer security reviews.
To understand our wider security service, visit our penetration testing services at Penva Security.
Use Cases
Most Australian businesses engage Penva Security for one of six clear cloud risk triggers; each maps to a compliance requirement, customer assurance request, cloud migration, or high-impact security event.
Coverage
Every Penva Security cloud engagement follows NIST SP 800-115, PTES, CSA Cloud Controls Matrix, CIS Benchmarks and cloud provider security best practices. We test cloud environments the way attackers do: by chaining IAM, storage, network, workload, secret and logging weaknesses to demonstrate real business impact.
Methodology
Aligned to NIST SP 800-115, CSA Cloud Controls Matrix, CIS Benchmarks, cloud provider security guidance, and the Penetration Testing Execution Standard (PTES).
STEP 01
We confirm the systems, testing goals and dates with you. You approve the scope and give us permission to begin.
STEP 02
Our testers check the agreed systems, investigate weaknesses and confirm their impact using controlled testing.
STEP 03
You receive a clear report explaining each finding, its severity and how to address it. We help your team understand the results.
STEP 04
Your team makes the changes. We then retest the identified issues and update the report to show their remediation status.
Outcome
With Penva's human-led, AI-assisted cloud penetration testing services, you can find exploitable cloud misconfigurations before attackers do, reduce privilege escalation risk, protect customer data, strengthen stakeholder confidence, and prove your cloud security posture with a clear, audit-ready report.
Compliance
Every Penva Security report is purpose-built to satisfy auditors, with the executive summary, CVSS 3.1 scoring, evidence appendix, and formal letter of attestation that compliance assessors require.
CASE STUDIES
How Penva Security helped businesses pass ISO 27001 and SOC 2 audits with penetration testing reports that satisfied assessors, closed critical gaps, and gave clients the confidence to scale securely.
CASE STUDY 01
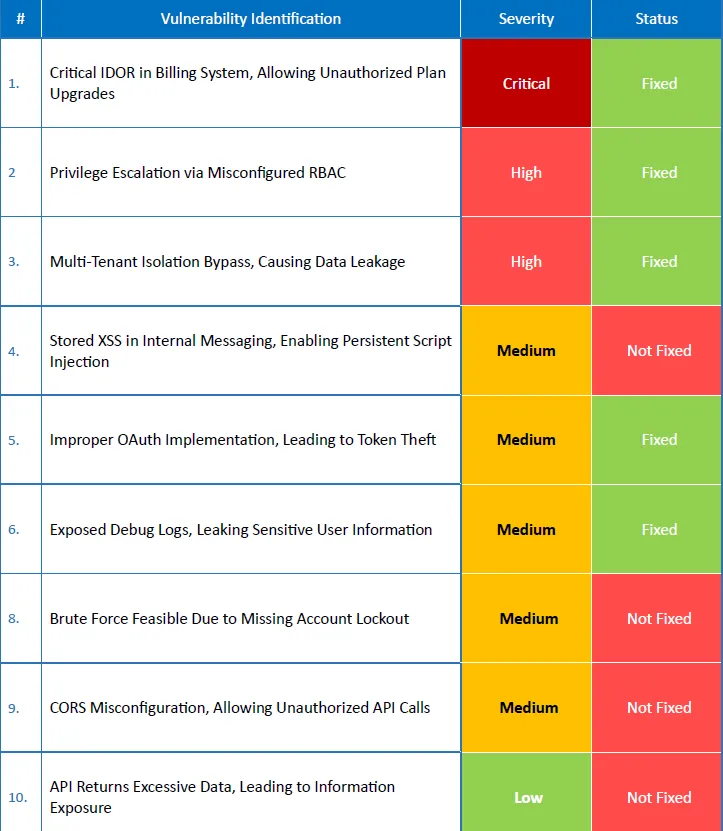
The penetration test for the Project Management Saas platform, initially conducted to achieve ISO 27001 compliance, uncovered and helped remediate several critical and high-risk vulnerabilities, including SQL injection and XSS flaws.
Although the client approached us only for compliance, we identified serious security gaps and helped secure their application. This proactive assessment demonstrates a strong commitment to data protection, risk mitigation, and adherence to internationally recognised security standards.
CASE STUDY 02
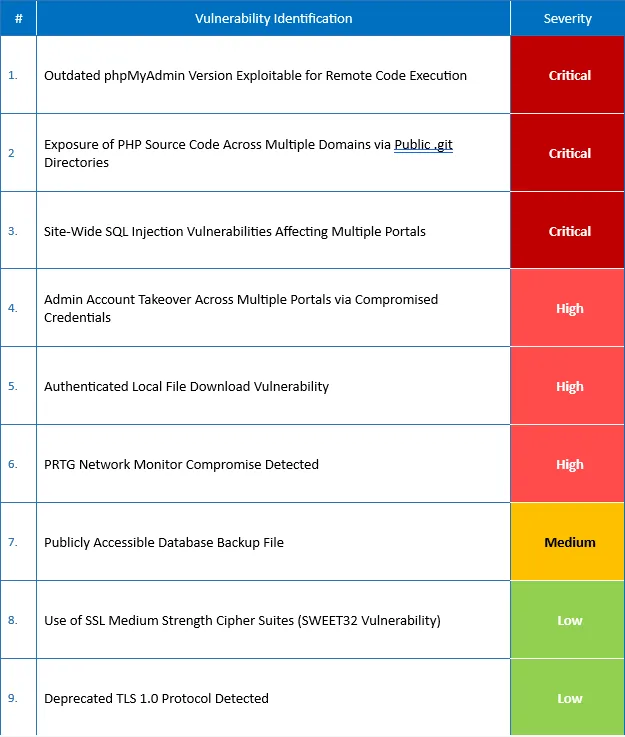
In pursuit of SOC 2 compliance, we conducted a comprehensive penetration test on the School Web Application, uncovering critical vulnerabilities such as outdated software and SQL injection across multiple domains.
The findings provide clear, actionable insights to strengthen the application's security posture, ensuring it meets SOC 2 trust principles, especially around data confidentiality, availability, and integrity.
CASE STUDY 03
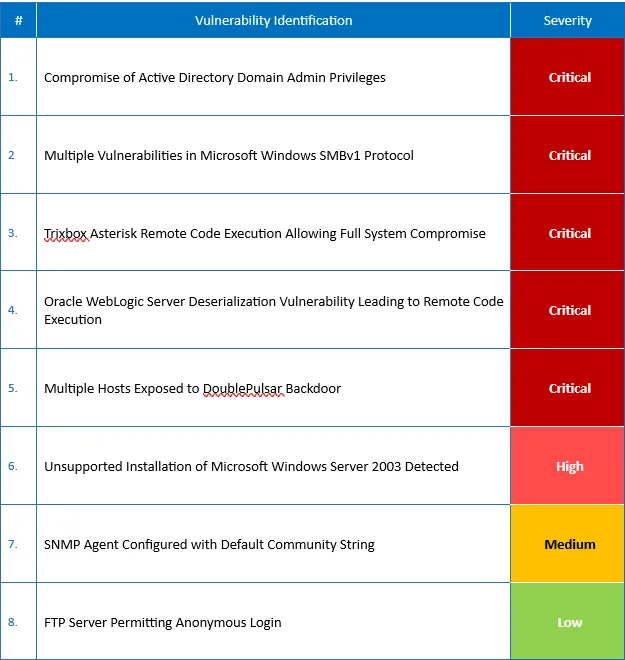
In a recent engagement with a financial institution, our internal network penetration test revealed multiple critical vulnerabilities that could have led to full domain compromise and unauthorised access to sensitive systems. We identified severe issues such as exposed administrative privileges, legacy protocols like SMBv1, and remote code execution flaws in key servers.
Our findings enabled the client to prioritise remediation, strengthen their internal security posture, and prevent potential exploitation that could have severely impacted operations and data integrity.
Why Penva Security
Get to know our testing approach, professional credentials and focus on findings your team can act on.
We have partnered with organisations across critical sectors, including finance, education, e-commerce, and healthcare, to enhance their security posture, meet compliance requirements, and confidently pass audits.
We've identified critical vulnerabilities in 70% of tested applications, including server compromises and leaked credentials, and helped secure their applications and infrastructure.
| Comparison criteria | Others | RecommendedPenva Security |
|---|---|---|
| Specialisation | Offer broad cybersecurity services with limited pentest focus | Focused and deeply specialised in penetration testing only |
| Pricing | High quotes with only a single actual resource on the project | Affordable and flexible pricing tailored to project needs |
| Transparency | No visibility throughout the penetration test engagement | Transparency via shared sheet tracking all test cases in real time |
| Collaboration | One-off report delivery after the penetration test is completed | Continuous collaboration with devs & providing a clean report at the end |
| Certifications | General security certs, often lacking pentest specialisation | Specialised pentest certs that take years to achieve |
| Brand Name | Certification | Certification Worth |
|---|---|---|
 | OSCP by Offensive Security | The OSCP (Offensive Security Certified Professional) is a highly regarded certification that validates practical penetration testing skills and is globally recognised by employers and regulators. |
| CREST Practitioner Security Analyst (CPSA) | CREST partners with national bodies in the UK, US, Australia, and Singapore, ensuring global recognition and compliance with the highest cybersecurity standards. |
 | HTB CPTS by Hack The Box | HTB Certified Penetration Testing Specialist (CPTS) validates hands-on penetration testing, vulnerability chaining and practical remediation reporting. It assesses how a tester identifies security weaknesses, demonstrates their impact and documents actionable findings. |
Our testers hold recognised professional certifications in hands-on penetration testing.
Client feedback
Read feedback from organisations that have worked with Penva Security on their penetration testing requirements.
"Penva Security provided a quick and efficient pentest report that satisfied our needs and certification criteria. I would highly recommend them for penetration testing, and will be using their services again in the future."
Clutch4.9 / 514 verified reviewsInstant Estimate Quote
Answer a few scoping questions to get a practical estimate for web, API, mobile, infrastructure, and cloud penetration testing.
Choose the main service you want quoted.
Team credentials
Our team holds industry-recognized pentest certifications that take years to achieve.
FAQ
Direct answers to the cloud security testing questions Australian businesses ask most often.
Cloud penetration testing is a controlled security assessment of your AWS, Microsoft Azure, Google Cloud, or hybrid cloud environment. Penva reviews cloud identity, permissions, exposed services, storage, networking, workloads, containers, serverless functions, secrets, and attack paths to identify exploitable weaknesses such as IAM privilege escalation, public data exposure, insecure security groups, leaked keys, misconfigured services, and lateral movement paths.
Cloud penetration testing in Australia typically starts from AUD $2,000 for a focused cloud security assessment. The final price depends on the number of cloud accounts or subscriptions, services in scope, IAM complexity, workloads, Kubernetes or container usage, serverless architecture, external exposure, and whether AWS, Azure, Google Cloud, or a hybrid environment is included. Penva provides a fixed-price quote after a free scoping call.
Most cloud penetration tests take 5 to 10 business days of active testing, plus 1 to 2 days for reporting. A small cloud environment with limited services may be assessed faster, while a complex multi-account AWS, Azure, or GCP environment with Kubernetes, CI/CD, IAM roles, and production workloads can take 2 to 3 weeks. Penva shares findings progressively so remediation can begin during testing.
Yes, when cloud systems store, process, or transmit sensitive business, customer, payment, or regulated data. ISO 27001, SOC 2, PCI DSS, APRA CPS 234, and enterprise procurement reviews commonly expect evidence that cloud infrastructure and applications are security tested. Penva provides audit-ready cloud pentest reports with risk ratings, evidence, business impact, remediation guidance, and retest validation.
A cloud posture scan checks cloud configuration against known best practices, such as public buckets, open ports, or weak settings. A cloud penetration test goes further by validating whether those weaknesses can be exploited, chained, and used to access data, escalate privileges, or move across cloud services. Penva combines cloud configuration review with attacker-led testing to show real business impact.
No. Penva delivers human-led cloud penetration testing. We use automated cloud posture tools and AI-assisted workflows only to support inventory, permission mapping, and coverage. Every cloud finding is manually validated by a tester before it is reported. This is important because cloud compromise often depends on chaining IAM permissions, exposed services, metadata access, secrets, and business context.
Penva follows NIST SP 800-115, PTES, CIS cloud benchmarks, cloud provider security guidance for AWS, Azure, and Google Cloud, and practical attacker-led cloud testing methodology. Our process covers scoping, cloud asset discovery, IAM and permission review, exposure analysis, workload testing, secrets review, exploitation, privilege escalation, lateral movement analysis, reporting, and remediation retesting.
Penva designs cloud testing to reduce risk to production workloads, customer data, and uptime. We avoid destructive actions unless explicitly approved, use read-only review where appropriate, coordinate testing windows for sensitive workloads, and validate high-risk issues safely. Testing is performed under agreed rules of engagement so security weaknesses can be confirmed without unnecessary disruption.
Yes. Every Penva fixed-price cloud penetration test includes one free retest within 60 days of the original engagement. After remediation, we re-check each issue and provide an updated report confirming whether the findings are fixed. This gives your team clear evidence for ISO 27001, SOC 2, PCI DSS, APRA, vendor security reviews, and internal risk sign-off.
Yes. Penva's testers hold recognised penetration testing certifications including CREST, OSCP, and HTB CPTS, with experience across cloud, web applications, APIs, networks, and identity environments. Cloud testing is performed by security professionals who understand both cloud configuration risk and real-world exploitation paths across IAM, workloads, secrets, and exposed services.
At minimum, cloud environments should be penetration tested annually and after significant changes such as new cloud accounts, new internet-facing services, IAM redesigns, Kubernetes deployments, CI/CD changes, mergers, migrations, or major infrastructure releases. Fast-moving cloud teams should test more frequently when sensitive data, regulated workloads, or customer-facing services are involved.
Penva commonly finds excessive IAM permissions, privilege escalation paths, public storage exposure, leaked cloud keys, exposed management interfaces, insecure security groups, vulnerable workloads, metadata service exposure, SSRF-to-cloud-token risk, weak CI/CD secrets handling, misconfigured containers, insecure serverless functions, and poor logging or alerting. The highest-impact issues usually involve identity abuse and access to sensitive cloud data.
Penva supports SaaS platforms, FinTech and payments providers, healthcare organisations, education platforms, e-commerce companies, professional services, and government supply-chain vendors across Australia. We work with teams in Melbourne, Sydney, Brisbane, Perth, Adelaide, and Canberra that need cloud testing for compliance, customer assurance, cyber insurance, or risk reduction.
Yes. Penva can sign a mutual NDA before any cloud architecture, account IDs, subscriptions, diagrams, credentials, permissions, or commercial information is shared. We can also work under your MSA, supplier agreement, data-handling requirements, or enterprise procurement process.
Let's talk security
Book a scoping call or share your systems, testing requirements and preferred timeline with our team.
Choose a time that works for you.
Share your scope, priorities and deadline.
Prefer to get in touch directly? [email protected]