
Australia’s Top‑Rated Penetration Testing Services
Our CREST certified experts combine manual testing with advanced methodologies to uncover vulnerabilities across applications, networks, APIs, and cloud systems. Forget about confusing reports with unclear findings – we provide a clear, accurate assessment backed by actionable recommendations for improvement.
- Certified Testers
- Security Compliance
- Manual Pentesting
Not sure which pentest you need?
Two taps and we’ll point you at the right one
Choose what needs to be protected. We’ll show the right test, with an indicative cost and timeline.
Meeting your Pentest Requirements
Achieve ISO 27001 or SOC 2 Compliance with Confidence
- Quick Delivery: Receive your compliance-ready report in as little as 7 days for ISO 270001, HIPAA, PCI DSS, APRA and SOC 2 compliance .
- Compliance-Focused Reporting: Our reports are purpose-built to meet compliance and audit needs, with an Executive Summary.
- Certified Experts: Our penetration testers hold CREST and OSCP certifications, that are recognized by regulatory bodies and compliance frameworks.
Earn Trust with a Professional Security Assessment
- Tell Us What You Need– Share your audit or compliance requirements, and we’ll create a tailored plan.
- Audit-Ready Reports: Get customized reports designed to support attestations for auditors or third-party vendors.
- Certified Experts: Our penetration testers hold CREST and OSCP certifications, that are recognized by regulatory bodies and compliance frameworks.
Defend your application and system with us
- Flexible Packages: Choose from weekly or monthly security testing plans that match your urgency and budget.
- Security With Confidence: Secure every asset and upskill your developers with 1:1 sessions focused on real attacker tactics and defense
- Penetration Testing Specialists: Our team is deeply focused on offensive security, with certifications like OSCP, CREST, and CRTO that prove real-world expertise.
Penetration Testing Process
Work closely with your team to identify exactly what needs to be tested, e.g. a website, mobile app, or internal system, and establish clear boundaries before testing begins. This phase ensures all stakeholders are aligned on what's in scope, reducing miscommunication and delays.
A penetration test execution phase validates real-world risk by actively finding, exploiting, and confirming vulnerabilities, then demonstrating impact with controlled proofs-of-concept. Results are cleaned up, evidence collected, and delivered as a prioritized report with remediation guidance.
Our pentest reports are designed to help you pass audits, with a clear executive summary, CVSS 3.1 severity ratings, and formal attestation to meet SOC2, ISO 27001, PCI DSS, and HIPAA compliance requirements.
Once the team resolves the identified vulnerabilities, a focused retest is performed to verify the fixes and deliver an updated report reflecting the remediation status.
Outcome of a Penetration Test

Penetration Test Report
A comprehensive document detailing identified vulnerabilities, potential risks, and prioritized recommendations.
Includes Executive summary alongside technical evidence like attack paths and severity scores (CVSS) for your IT team.

Remediation Plan and Support
Provides step-by-step instructions and direct collaboration with the dev team to implement fixes, ensuring risks are eliminated.
If required, receive a follow-up report confirming all issues are resolved for accountability and compliance.

Certification of Testing
Official validation that your systems were rigorously tested and meet industry security standards.
Offers formal documentation (e.g., compliance with GDPR, PCI DSS) to demonstrate due diligence to clients, auditors, or regulators.
Hire Penetration Testers to Secure Your Business
Tell us what you need or check an estimated pentest price. Click the link below
Our Case Study
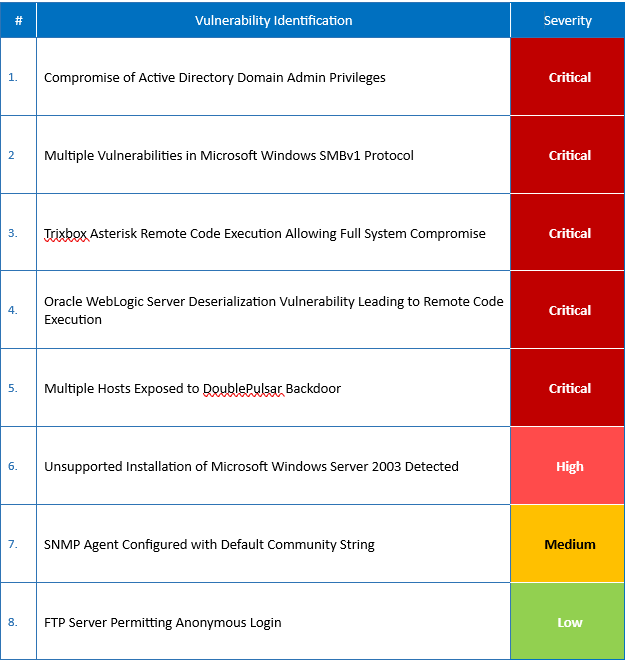
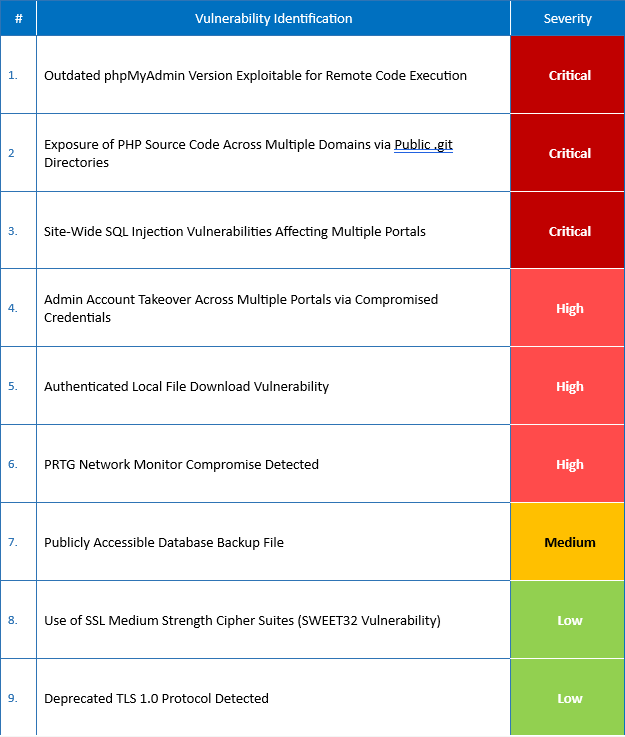
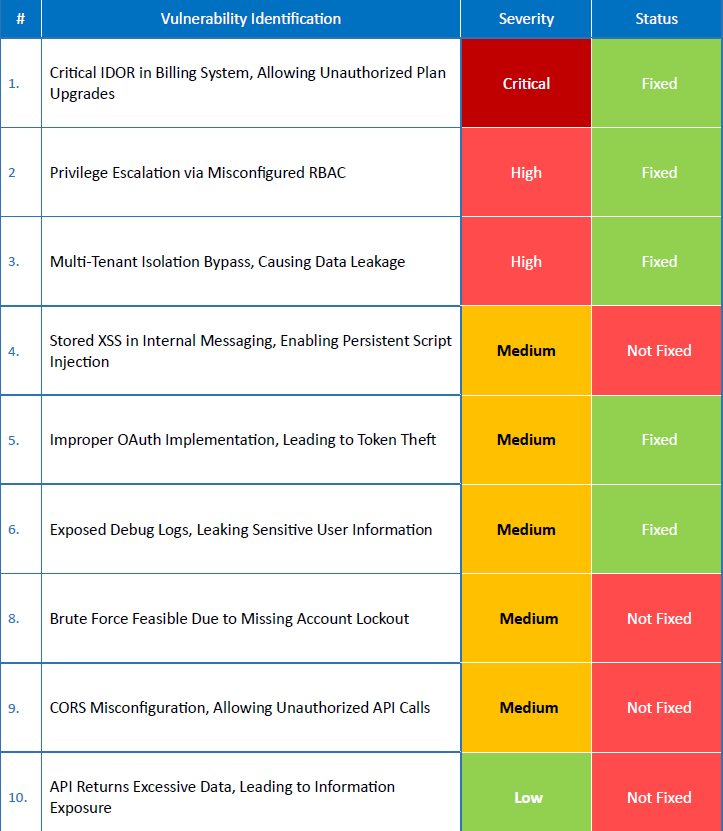
Although the client approached us only for compliance, we identified serious security gaps and helped secure their application. This proactive assessment demonstrates a strong commitment to data protection, risk mitigation, and adherence to internationally recognized security standards.
The findings provide clear, actionable insights to strengthen the application’s security posture, ensuring it meets SOC 2 trust principles, especially around data confidentiality, availability, and integrity.
Our findings enabled the client to prioritize remediation, strengthen their internal security posture, and prevent potential exploitation that could have severely impacted operations and data integrity.
Why Choose Us
Our Packages
Fixed-Price Pentest
From A$2,000 / engagement
Pre-defined scope with clear deliverables – ideal for compliance-driven engagements.
- Human-led + AI-accelerated testing
- Audit-ready PDF report (ISO / SOC 2 / PCI DSS)
- Free retest within 60 days
- Letter of attestation
- 1:1 remediation walkthrough
Pay-As-You-Go
- Ongoing human + AI testing support
- Real-time issue notifications
- Direct Slack / Teams collaboration
- Test new features as they ship
- Pause or resume any time
Reviews and Clients
Michael Wendland
Partner at Bonsai
Reliable and professional penetration testing partner
Penva Security provided a quick and efferent pentest report that satisfied our needs and certification criteria. I would highly recommend them for penetration testing, and will be using his services again in the future.

Stuart Cox
Creative Director at NorthBase
Professional, communicative, and highly reliable testers
Penva Security conducted a penetration test of our webapp and produced a report of security issues. The team was professional and communicated well throughout, including giving us the expected timeline for the work and keeping us up-to-date as we progressed. The report was well written and I can recommend them to anyone looking for penetration testing.
Daniel Scocco
Founder at InstaDelivery
Working with third or forth time with Penva Security
This is the third or fourth time we work with Penva Security. They always delivers timely and great work. One of the best security experts I know.
Get an Instant Penetration Testing Estimate
Answer a few scoping questions to get a practical estimate for web, API, mobile, infrastructure, and cloud penetration testing.
What type of penetration testing do you need?
Choose the main service you want quoted.
Edit option values
Use this table to assign a dollar value to each option. Open this panel with ?penvaPricing=1 at the end of the page URL.
For permanent changes, copy the pricing config and paste it into the PRICE_OVERRIDES section inside this Elementor HTML widget. Front-end prices are only used to display an estimate and should not be treated as a fixed quote.
Our Team's Certification
Our team holds industry-recognized pentest certifications that take years to achieve.


Frequently Ask Question
What is a penetration testing?
How much does penetration testing cost in Australia?
What are the key stages in a penetration testing methodology?
Here’s a simple and concise explanation of the pentest methodology in numbered steps:
Planning and Scope Definition: Define test objectives, target systems, and agree on a detailed quotation with the client to set clear expectations.
Execution of Penetration Test: Use certified penetration testing tools and manual techniques to gather information, identify vulnerabilities, and simulate real-world cyberattacks to exploit weaknesses.
Reporting: Deliver a comprehensive penetration testing report that highlights discovered security flaws, risk ratings, and actionable remediation recommendations.
Remediation and Retesting: Collaborate with the client to fix vulnerabilities and perform retesting to confirm the effectiveness of security controls.
Are you compliant with regulatory standards?
Will you conduct Manual testing or use Automated scanners?
How long does a penetration test take?
Why should you trust us?
Please explore our reviews and see feedback from past clients.
What is cybersecurity penetration testing?
It’s a simulated cyberattack to identify vulnerabilities in your systems before attackers exploit them.
Why hire penetration testers from Penva Security?
Our CREST‑certified experts provide manual, in‑depth testing with actionable remediation plans.